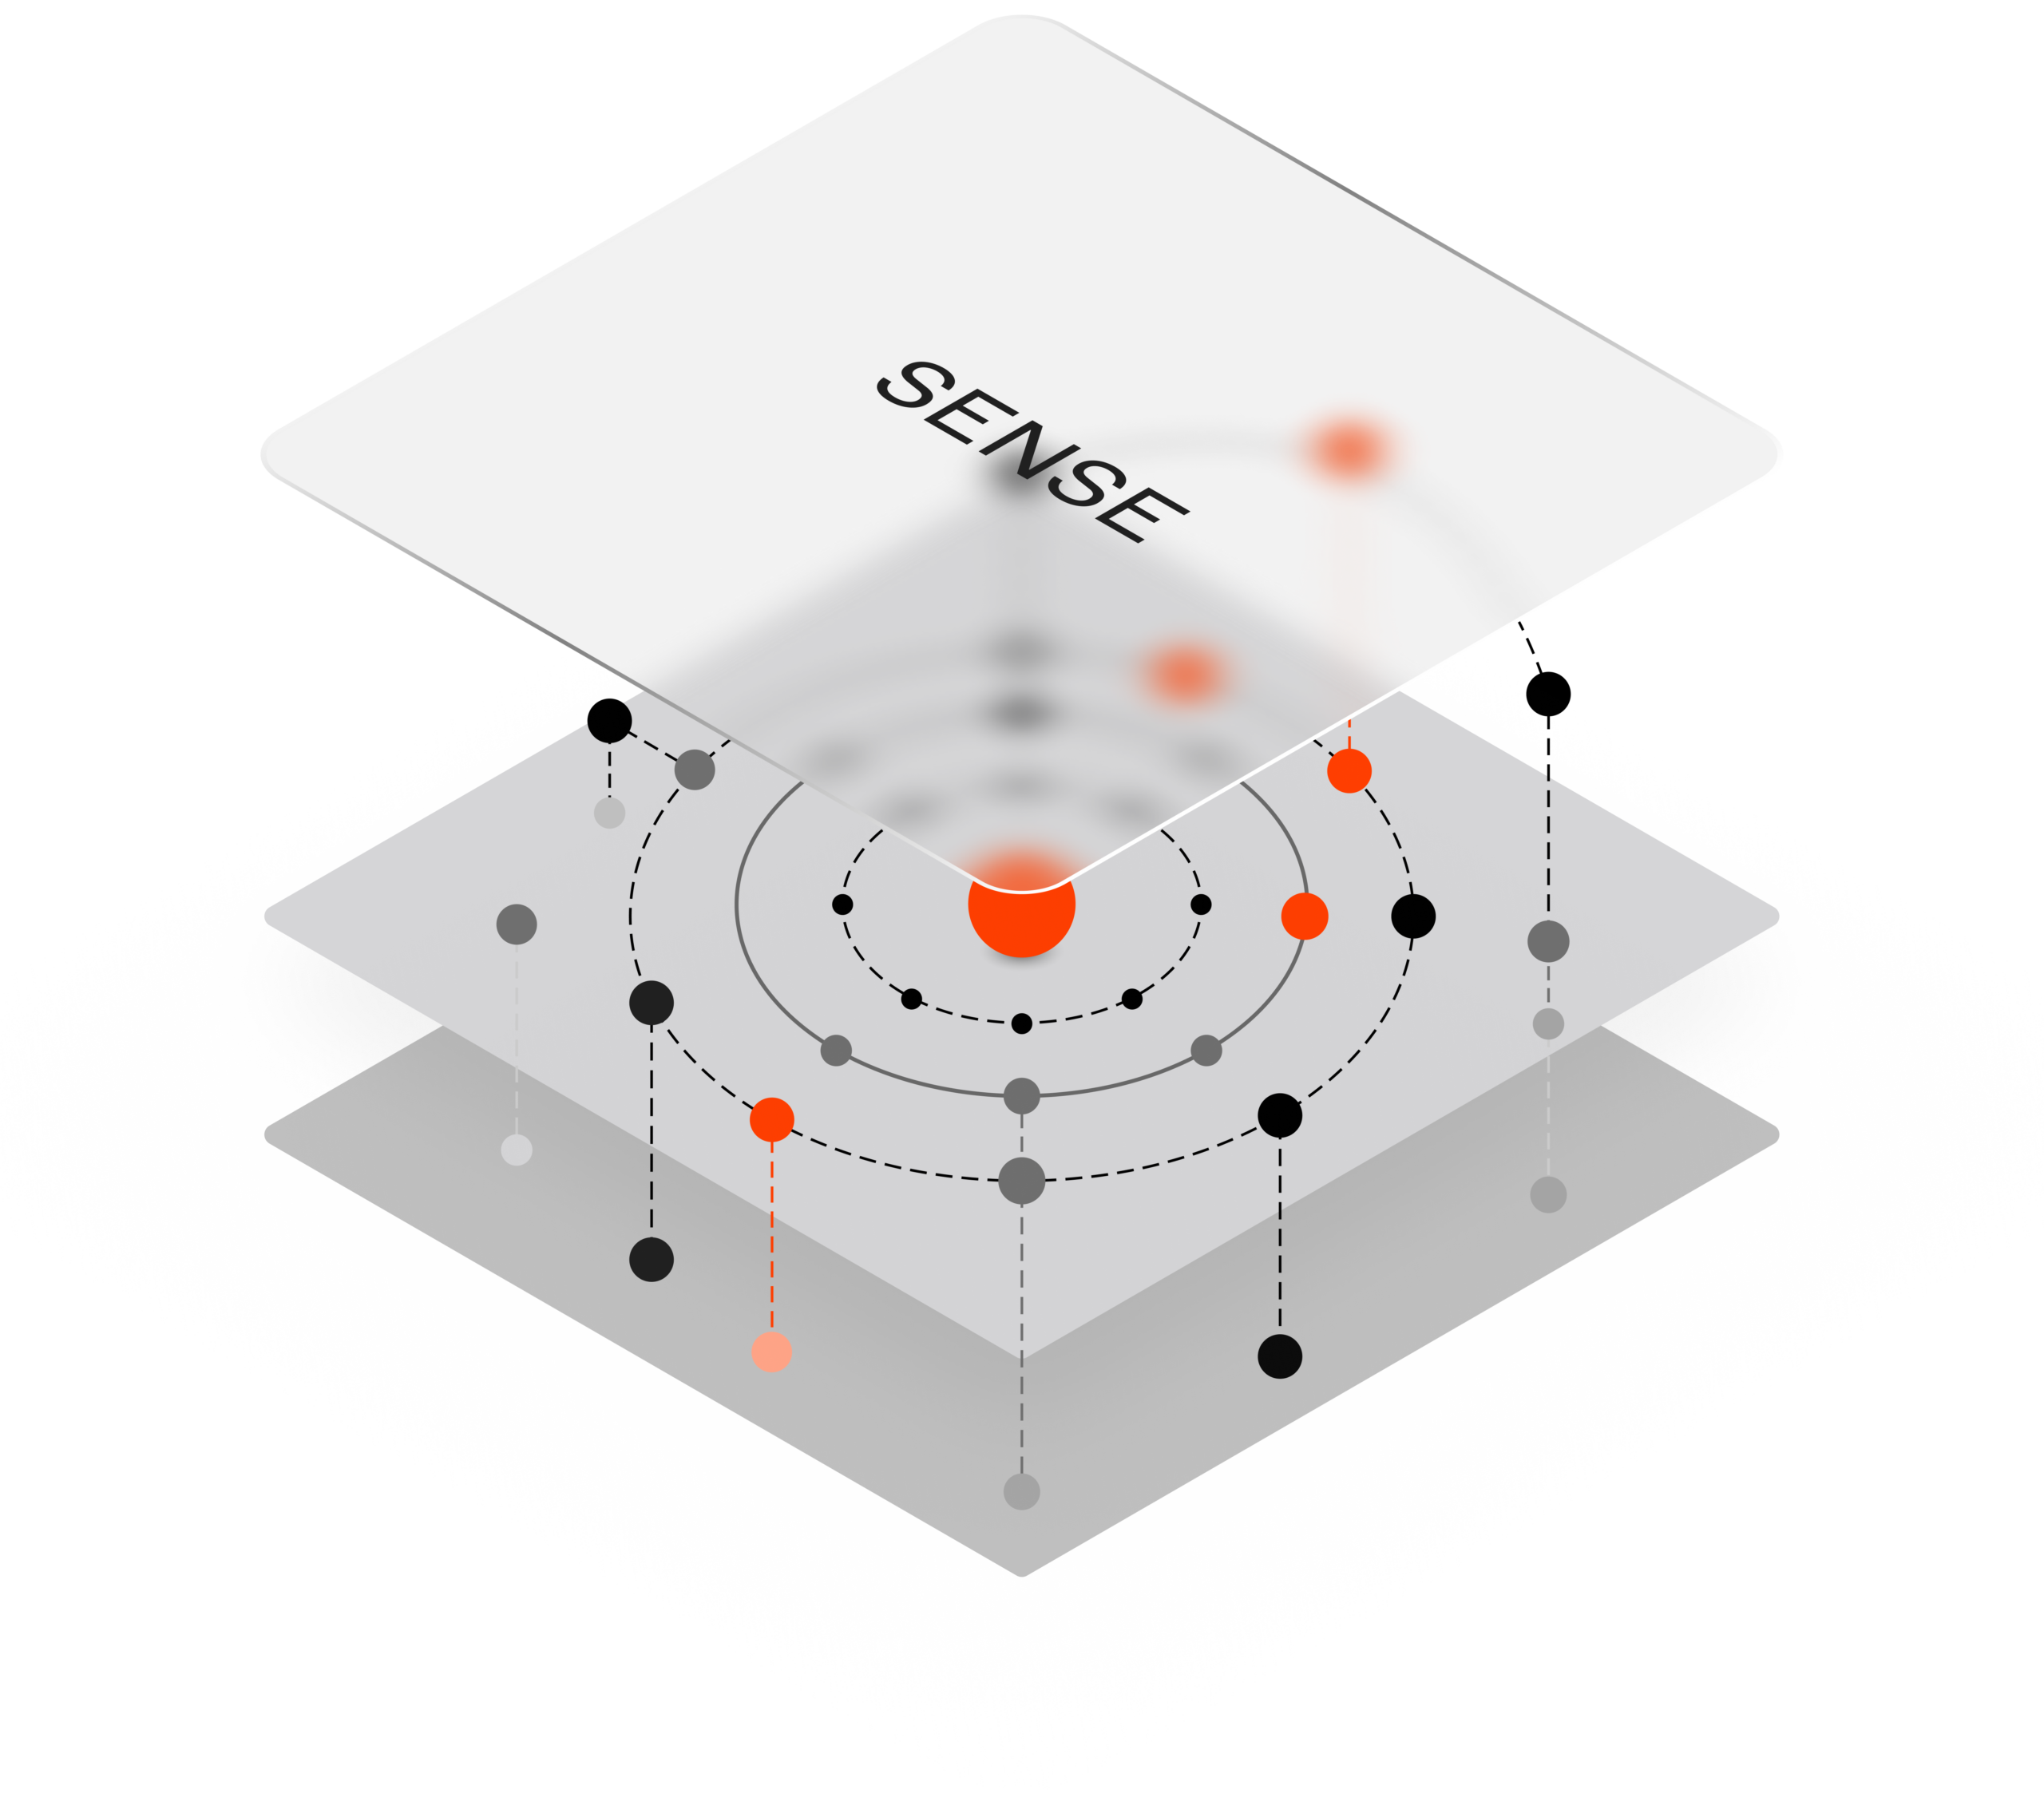
Sense – See the risks before they become reality.
Identity Security begins with understanding where risks arise. KOGIT analyses existing IAM structures, regulatory requirements, technological developments and new risks arising from cloud, automation, AI and Non-Human Identities.
This creates a clear picture of the situation:
-
Which topics are critical?
-
Which vulnerabilities affect security, compliance or operations?
-
And which measures should be prioritised?
Detect what matters.
Many organisations have organically grown permission structures, complex system landscapes and unclear responsibilities.
Sense helps to assess this initial situation and to detect relevant signals early.
KOGIT does not view Identity Security in isolation from a purely technical perspective, but in the interplay of organisation, processes, governance and risk. The goal is a robust basis for deciding on the next steps.
Typical focus areas:
-
IAM and Identity Security assessments
-
Risk and maturity assessments
-
Analysis of critical entitlements
-
Assessing governance and compliance requirements
-
Classification of cloud, SaaS and hybrid identity landscapes
-
Analysis of Non-Human Identities, service accounts and technical access
-
Preparation of roadmaps, modernisation and migration

Outcome:
After Sense, organisations know where their greatest Identity Security risks lie, which topics have priority and which areas should be examined in greater depth.

Guidance and support tailored to your needs
E-mail our team E-mail our team
Prefer to speak with
our team directly?
View phone number
